What is Sectigo Edge?
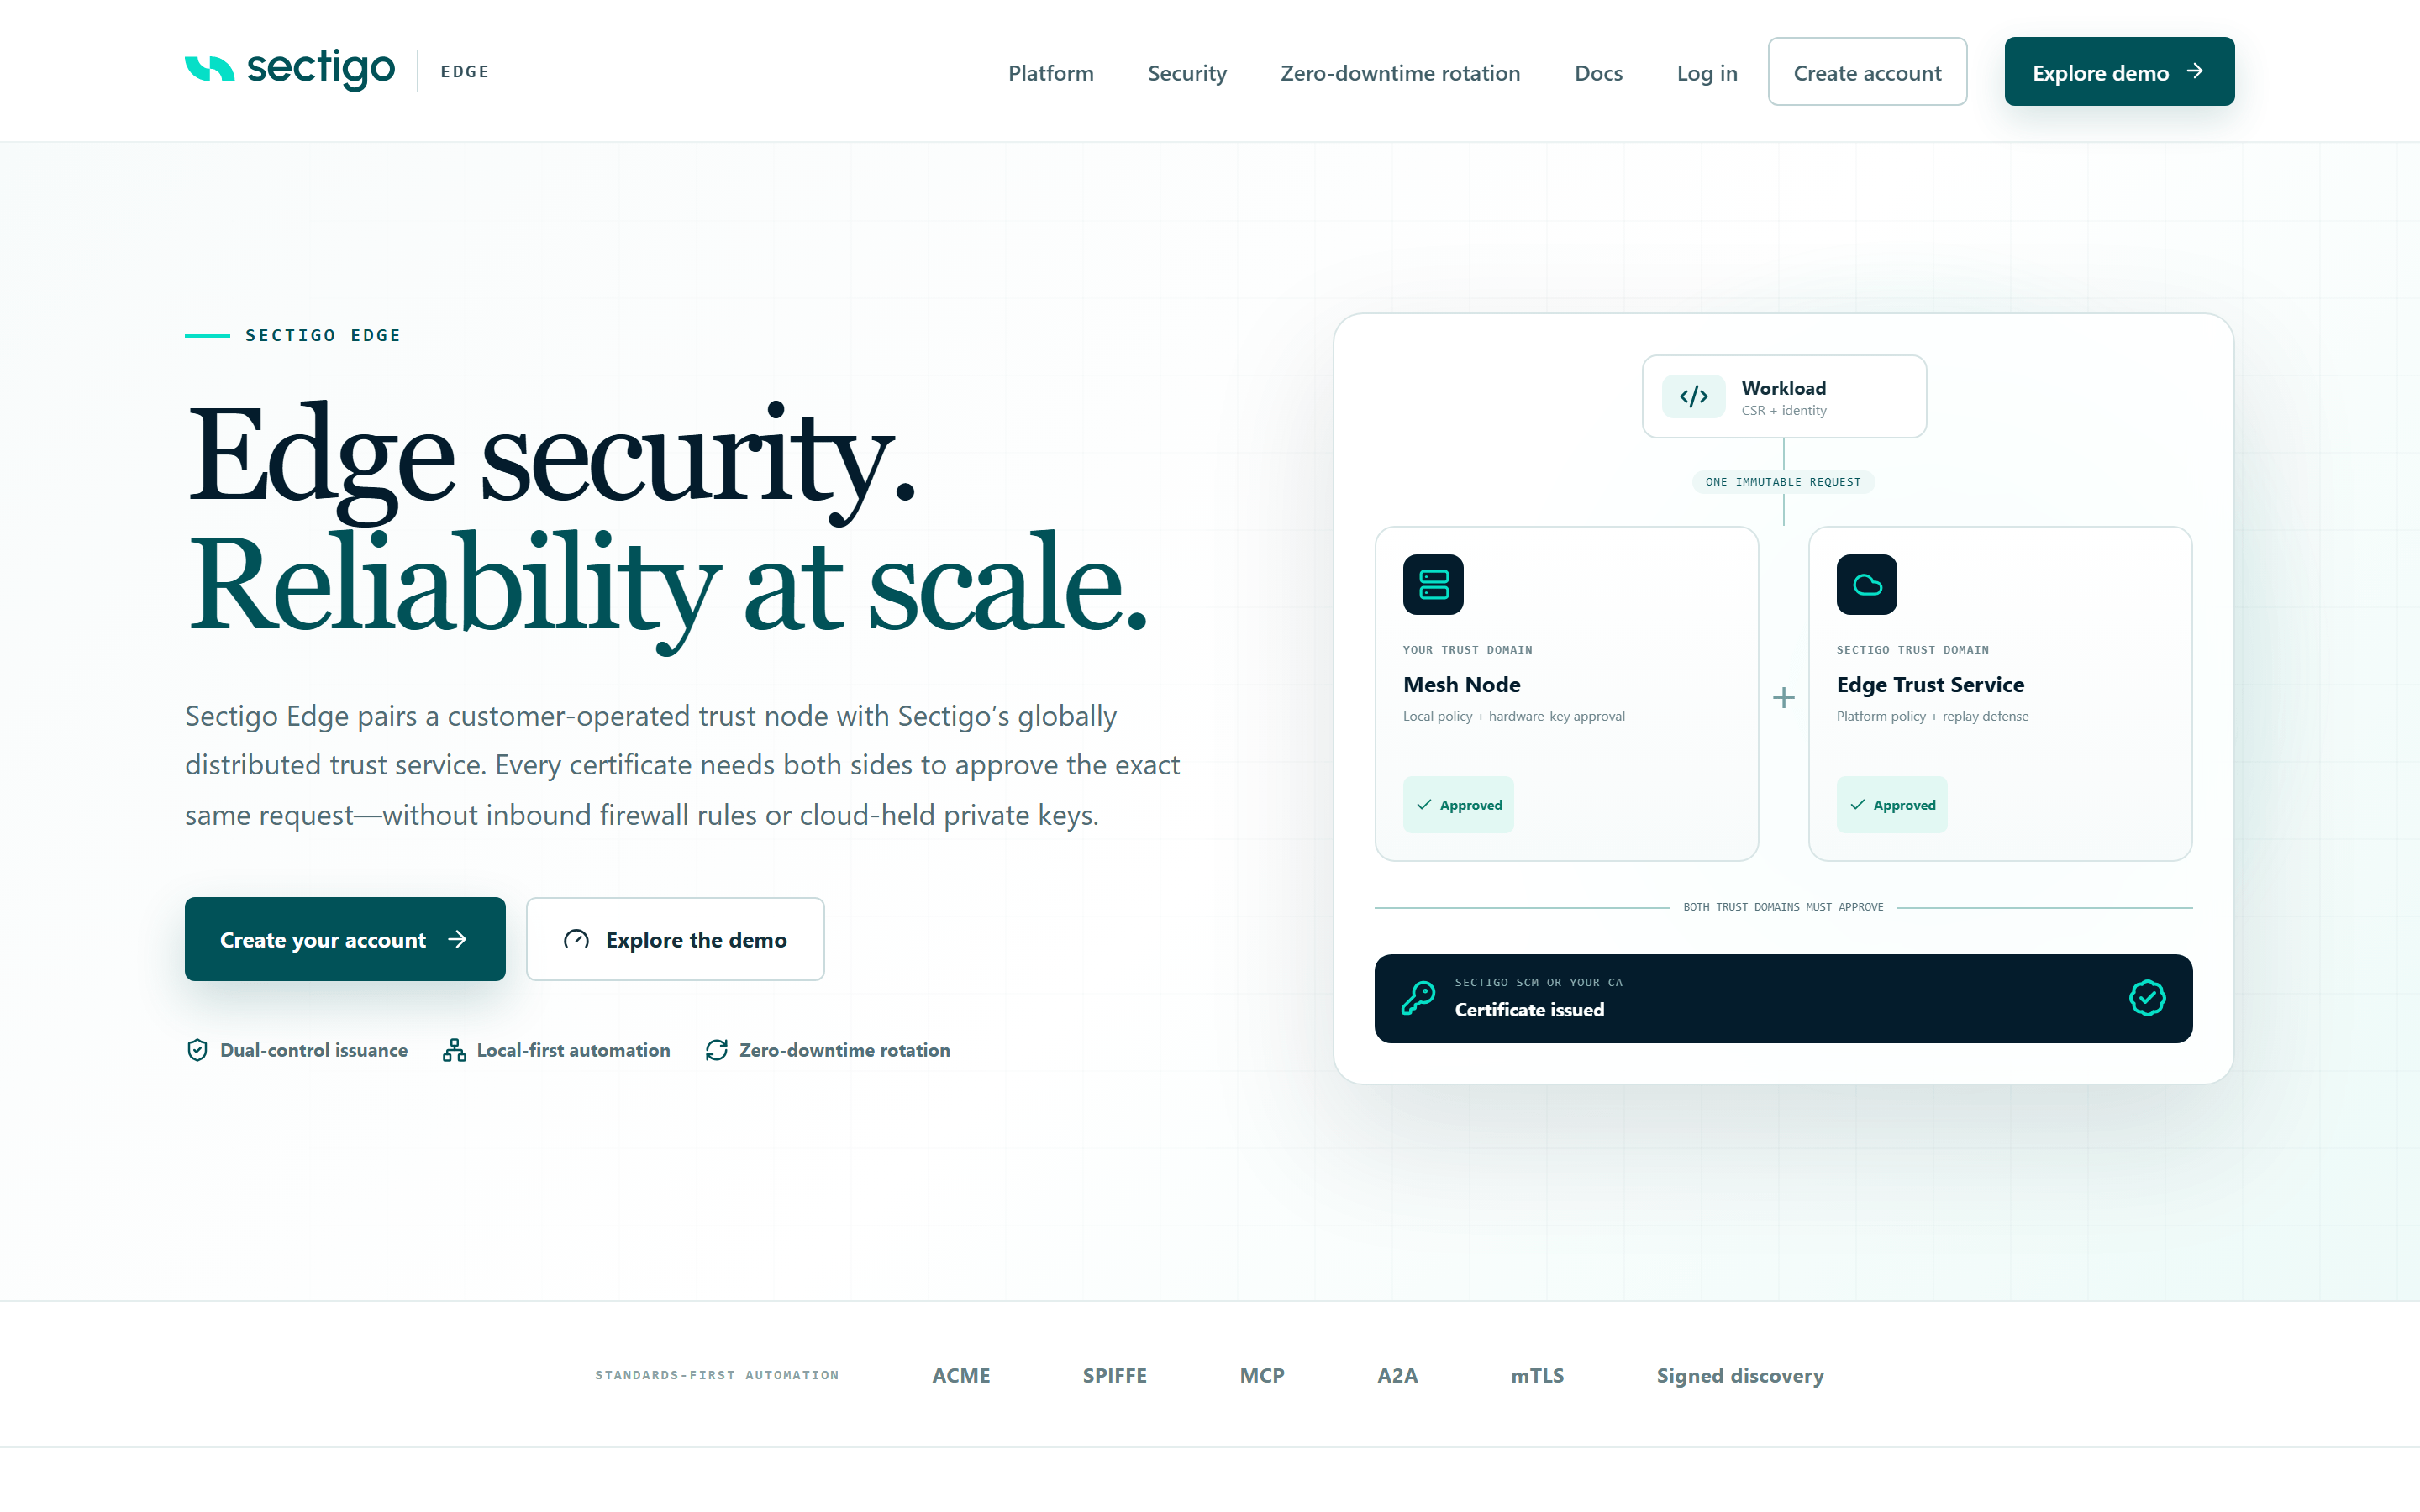
Sectigo Edge is a private PKI service that makes every certificate a two-party decision. A trust node that you run in your own environment (a Mesh Node) and Sectigo's globally distributed trust service must both approve the exact same request before your certificate authority signs anything.
The problem it solves
Traditional hosted PKI concentrates authorization in one administrative plane. If that plane is compromised, an attacker can issue trusted certificates.
Sectigo Edge splits that authority:
- Your environment is a required participant. Your Mesh Node evaluates every request against your policy, locally.
- Sectigo independently checks the same request. The edge evaluates the identical, immutable transaction and keeps its own policy and lifecycle controls.
- Only dual-approved requests reach the signer. Your CA (Sectigo Certificate Manager or a CA you bring) signs only when both sides agree.
If one side is compromised, the other side still says no.
How an issuance works
| Step | Who | What happens |
|---|---|---|
| 1. Workload requests | Your workload | Authenticates locally and asks for a tightly scoped identity. |
| 2. Your node decides | Your Mesh Node | Your policy evaluates the exact CSR, SANs, algorithm, validity and requester. |
| 3. Sectigo decides | Sectigo Edge | Independently evaluates the same immutable transaction digest. |
| 4. Your CA signs | Your CA | Only dual-approved evidence reaches Sectigo SCM or your protected CA signer. |
The main pieces
What you can do with it
- Issue and inventory certificates for services, workloads and AI agents, with every request evaluated by both trust domains.
- Rotate without downtime. Optional dual-slot mode stages the new certificate beside the one already serving, checks it, then promotes it atomically. Failed checks leave the active certificate untouched.
- Plan cryptographic migrations, including post-quantum readiness, using evidence of what your endpoints can actually consume.
- Prove what happened. Every issuance produces signed, hash-chained audit evidence on both sides that you can export.
- Contain incidents with an issuance kill switch and break-glass controls that require a second, independent approver.
Where it fits
Sectigo Edge does not replace your CA. It sits between your workloads and your signing authority:
- Workloads keep using open protocols (ACME, EST, SPIFFE, mTLS) against a nearby Mesh Node.
- Your CA keeps signing, but only for requests that both your node and Sectigo approved.
- Your identity provider can be connected for enterprise SSO. A Sectigo Edge email-and-password account (with MFA) is also available.
The live product demo runs the full console against isolated sample data (Acme Corporation). It never grants production access.
Next steps
- Learn the vocabulary in Concepts & terminology.
- Create your account.
- Verify your email and domain, then wait for workspace approval.
- Sign in for the first time and set up MFA.